Information Systems Risk Assessment for a Public Organization
Key Objectives
- Identify vulnerabilities in the information systems and processes of the organization in order to raise the Cyber Security standards
Our Approach
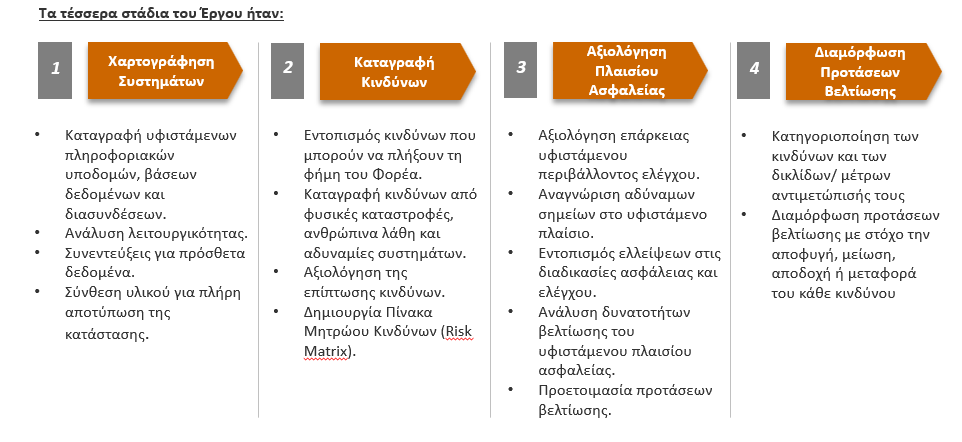
- Mapped all the systems and sub-systems of the organisations
- Identified the current risk mitigation measures and controls
- Evaluated the current risk mitigation measures
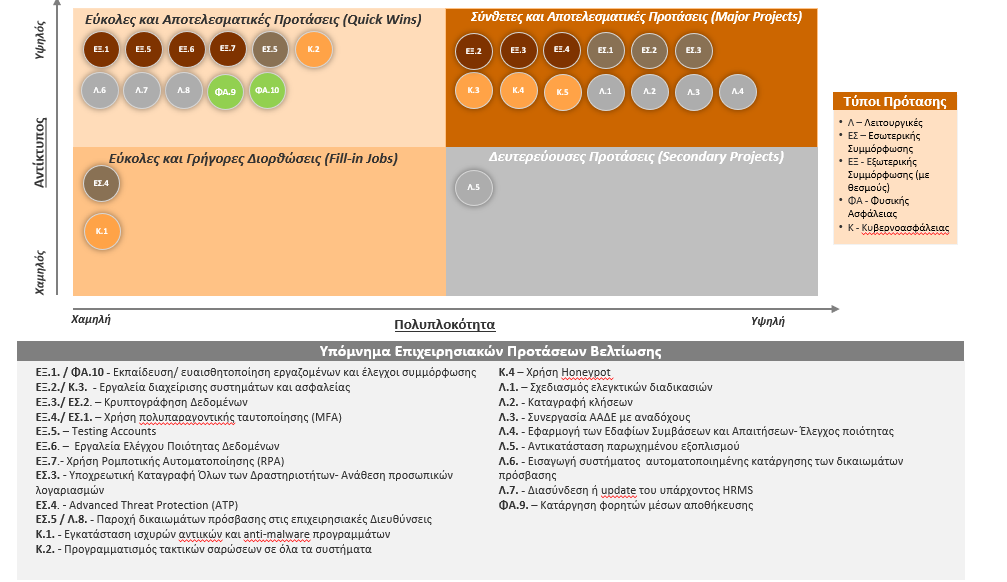
- Designed new risk mitigation measures and controls in areas where the existing ones did not provide adequate control
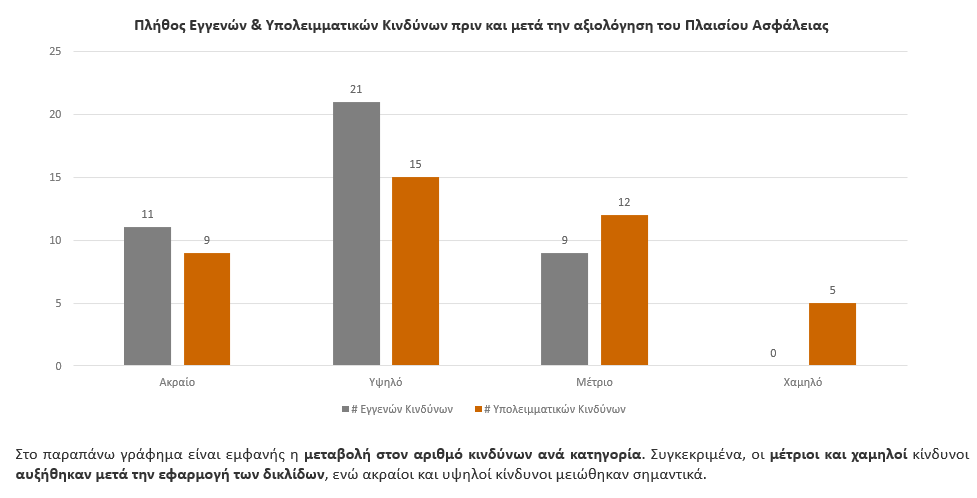
- Performed a Risk Assessment incorporating the newly designed controls and risk mitigation measures
Impact for our Client
- Developed a comprehensive Risk Assessment Framework for the organization